What is included?
Guided work process, 13 editable work tools, SCMS Cockpit, 9 AI assistants and documentation.
Manage supplier, SaaS and component risks from criticality through monitoring in one connected work status.
For procurement, supply chain, information security, product security, quality and compliance teams that need to handle supplier and third-party cybersecurity in a structured, case-based way.
Guided work process, 13 editable work tools, SCMS Cockpit, 9 AI assistants and documentation.
Criticality, due diligence, contracts, evidence, vulnerabilities, incidents, monitoring and approval.
No legal advice, supplier audit, automatic classification or approval.
Ready for you. Ready for your AI.
You do not have to build the entire working structure from scratch – not even with your AI. The Kit already includes these materials: A connected supplier-security workflow with an Excel cockpit, editable supplier records, contracts/evidence tools and a worked example. This prepared foundation supports the practical task: Assess supplier criticality, due diligence, requirements, SBOM/VEX, incidents, corrective actions, monitoring and evidence in one supplier case.
With your own appropriately approved AI assistant, you can work on the actual case, adapt the supplied materials and review information gaps rather than first designing a new workflow. Your team provides verified information and makes the decisions; the Practice Kit provides the prepared working framework.
The assistant can use a defined supplier case and existing work tools to expose missing supplier answers, evidence gaps and follow-up actions instead of constructing a separate supplier-review system. The product includes the following AI-related working support: Nine separate system-neutral AI assistants for scope, criticality, due diligence, contract gaps, SBOM, vulnerabilities/VEX, supplier incidents, monitoring and audit evidence.
Use the relevant supplied files with an AI system approved by your organisation, provided it supports the formats and data-handling requirements. AI support is optional; an AI service or subscription is not included. Supplier facts, technical vulnerability impact, contractual choices and release or escalation decisions require human verification.
Supplier information, security requirements, evidence, vulnerabilities, incidents and decisions are often spread across teams and files.
A connected working system for traceable assessment, documentation, monitoring and management decisions.
Connect scope, criticality, due diligence, evidence, measures and decisions.
Use editable templates and the SCMS Cockpit for the actual working process.
Keep changes, vulnerabilities, incidents, reviews and approval status visible.
Criticality, due diligence, security requirements, contracts, SBOM/VEX, incidents, monitoring and evidence are already connected in one working framework. This reduces the need to design a supplier-cybersecurity work system from scratch.
Prepared processes, work tools and evidence structures help reduce internal research and setup effort.
Existing specialist knowledge can be transferred directly into a structured working process inside the organisation.
Legal, technical or other specialist questions remain with the appropriate experts. External support can be focused on the points that require individual assessment or specialist decisions.
Use the Practice Kit to structure supplier, service and component cases. It does not replace a legal, technical or case-specific assessment.
Establish the relevant dependency, service context, criticality and assessment boundary.
Document supplier information, evidence gaps, assessment and required follow-up.
Structure requirements, notification paths, evidence and review expectations.
Link external notifications, components, versions, assessment status and internal escalation.
Keep reassessment triggers, measures, reviews and management decisions traceable.
Connected work tools for supplier, service and technical dependency cases.
Orientation, sequence and working logic for the end-to-end process.
Templates and variants for scope, criticality, due diligence, requirements, evidence and lifecycle work.
Central working file for registers, status, reviews, measures and management overview.
System-neutral assistive workflows for structuring and completeness review.
Start guidance, worked example, licence, sources, manifest and change log.
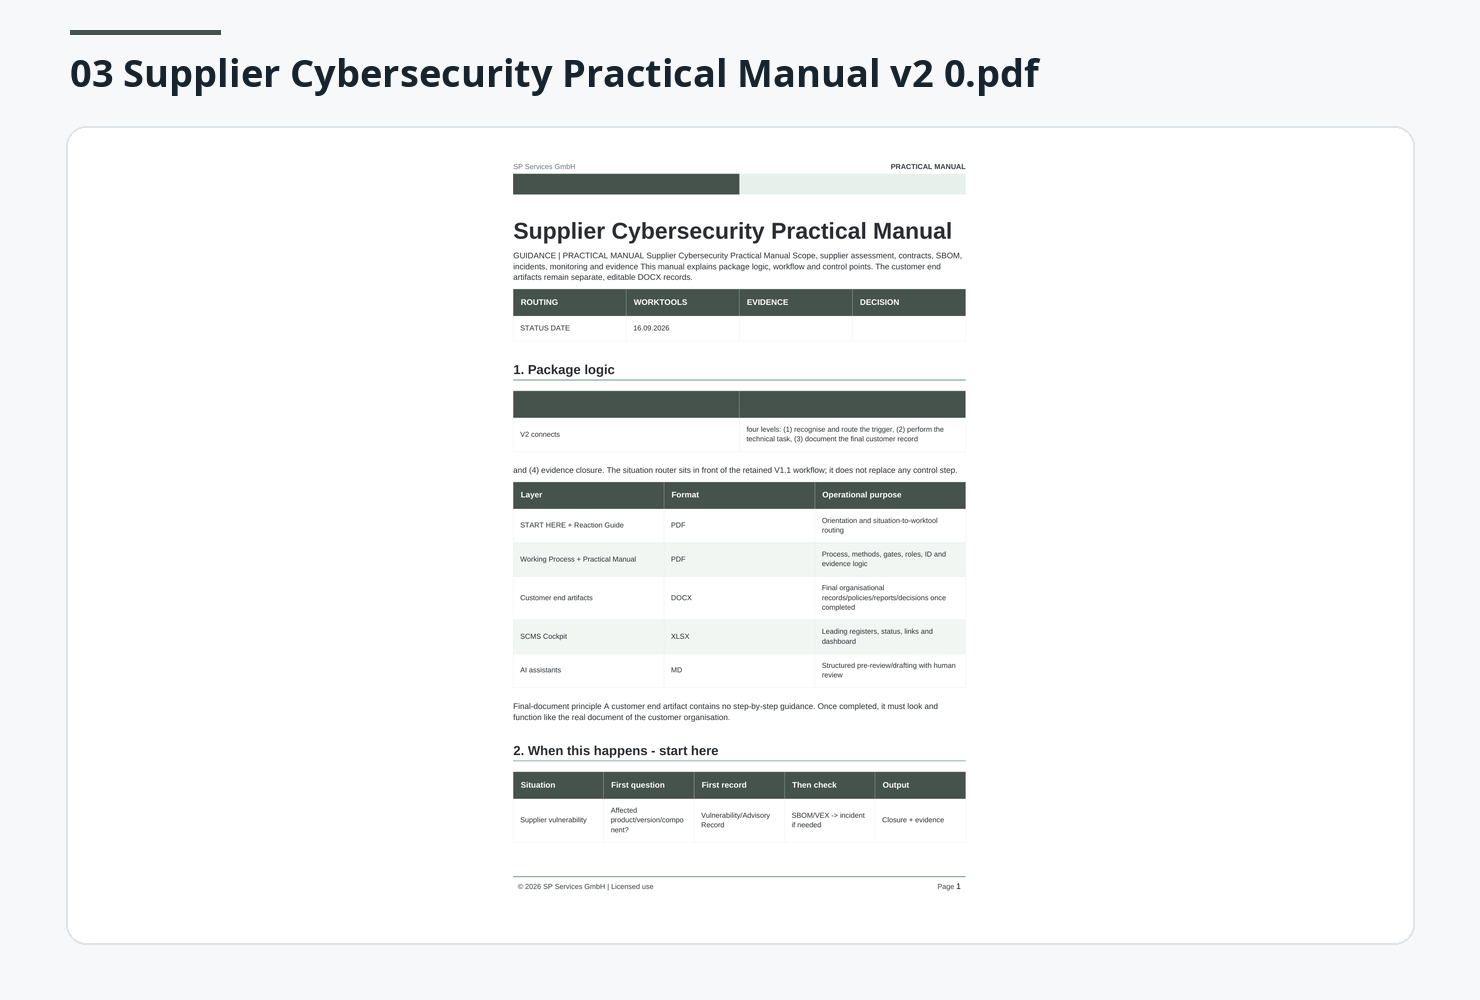
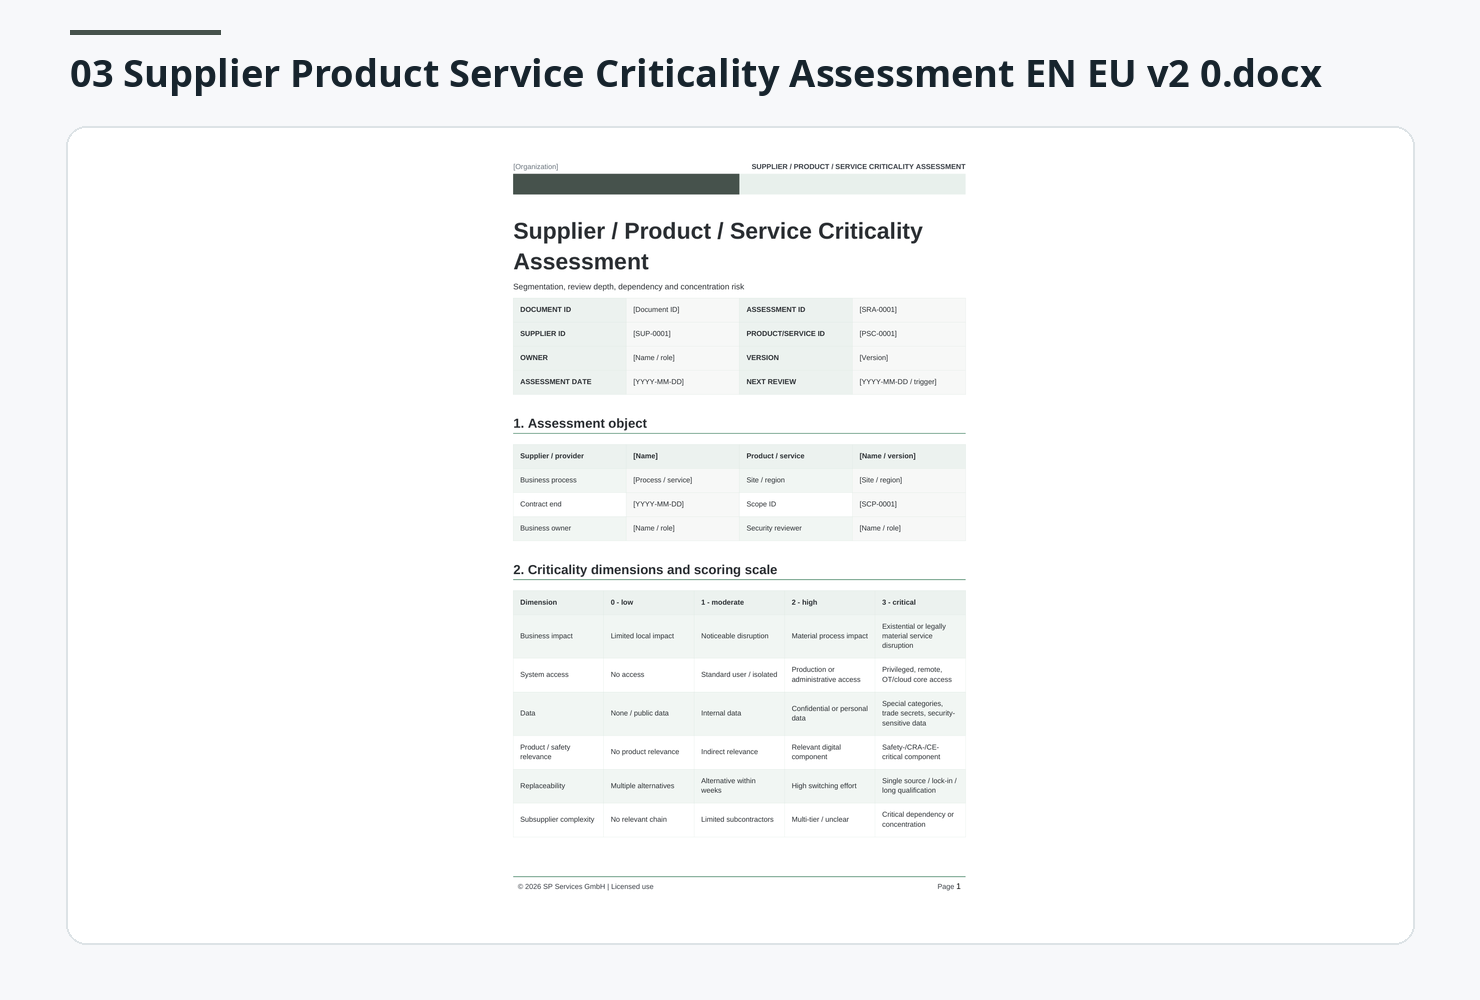
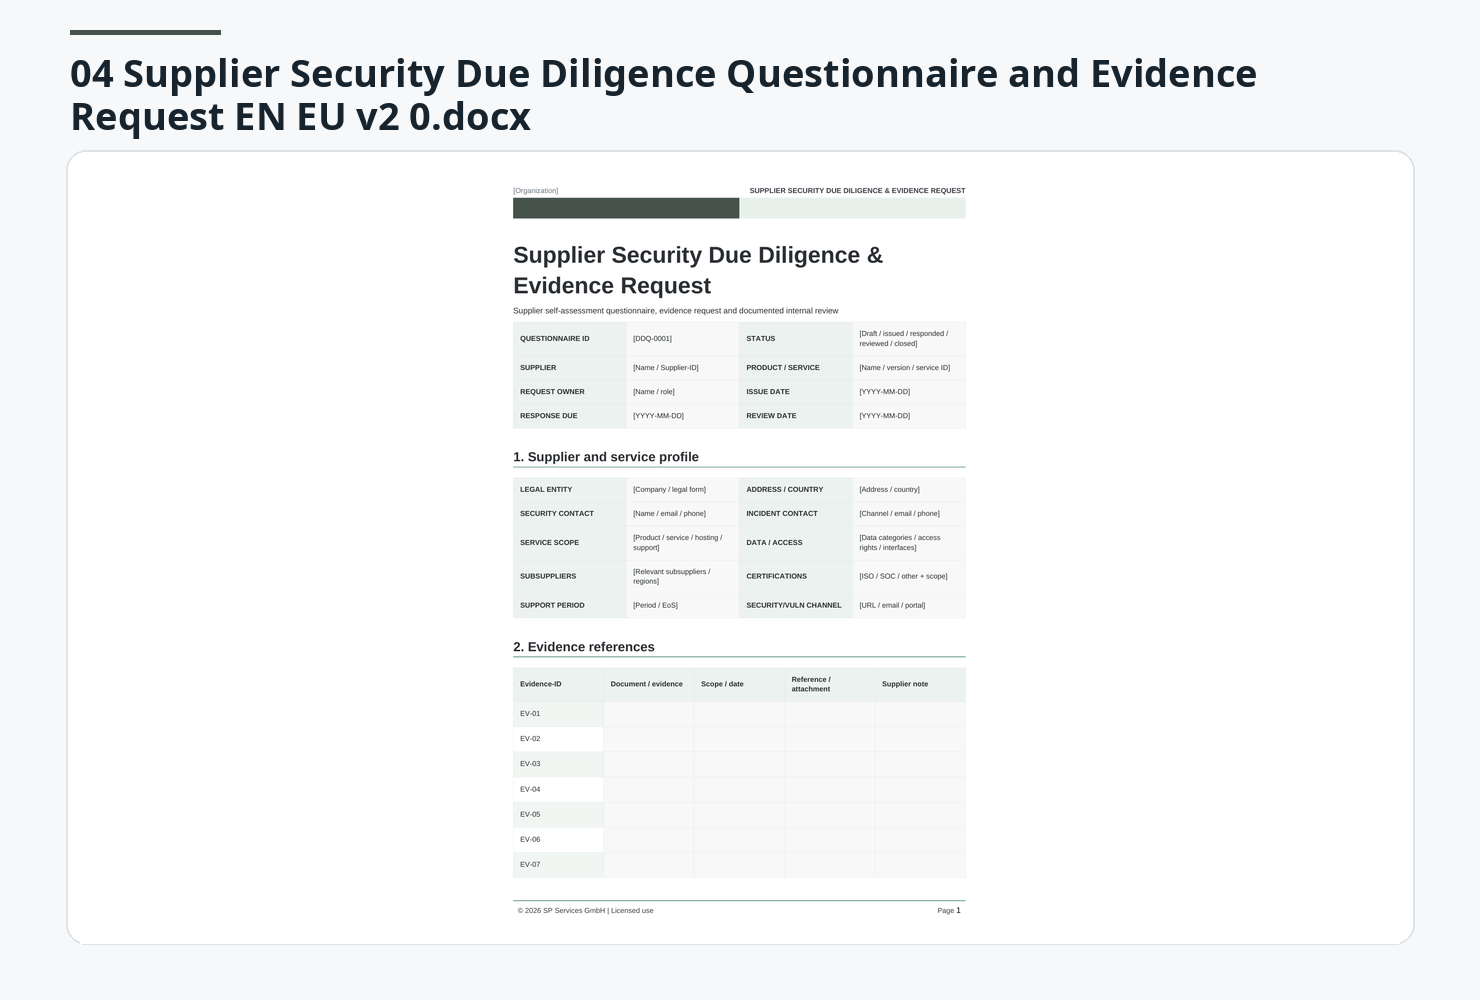
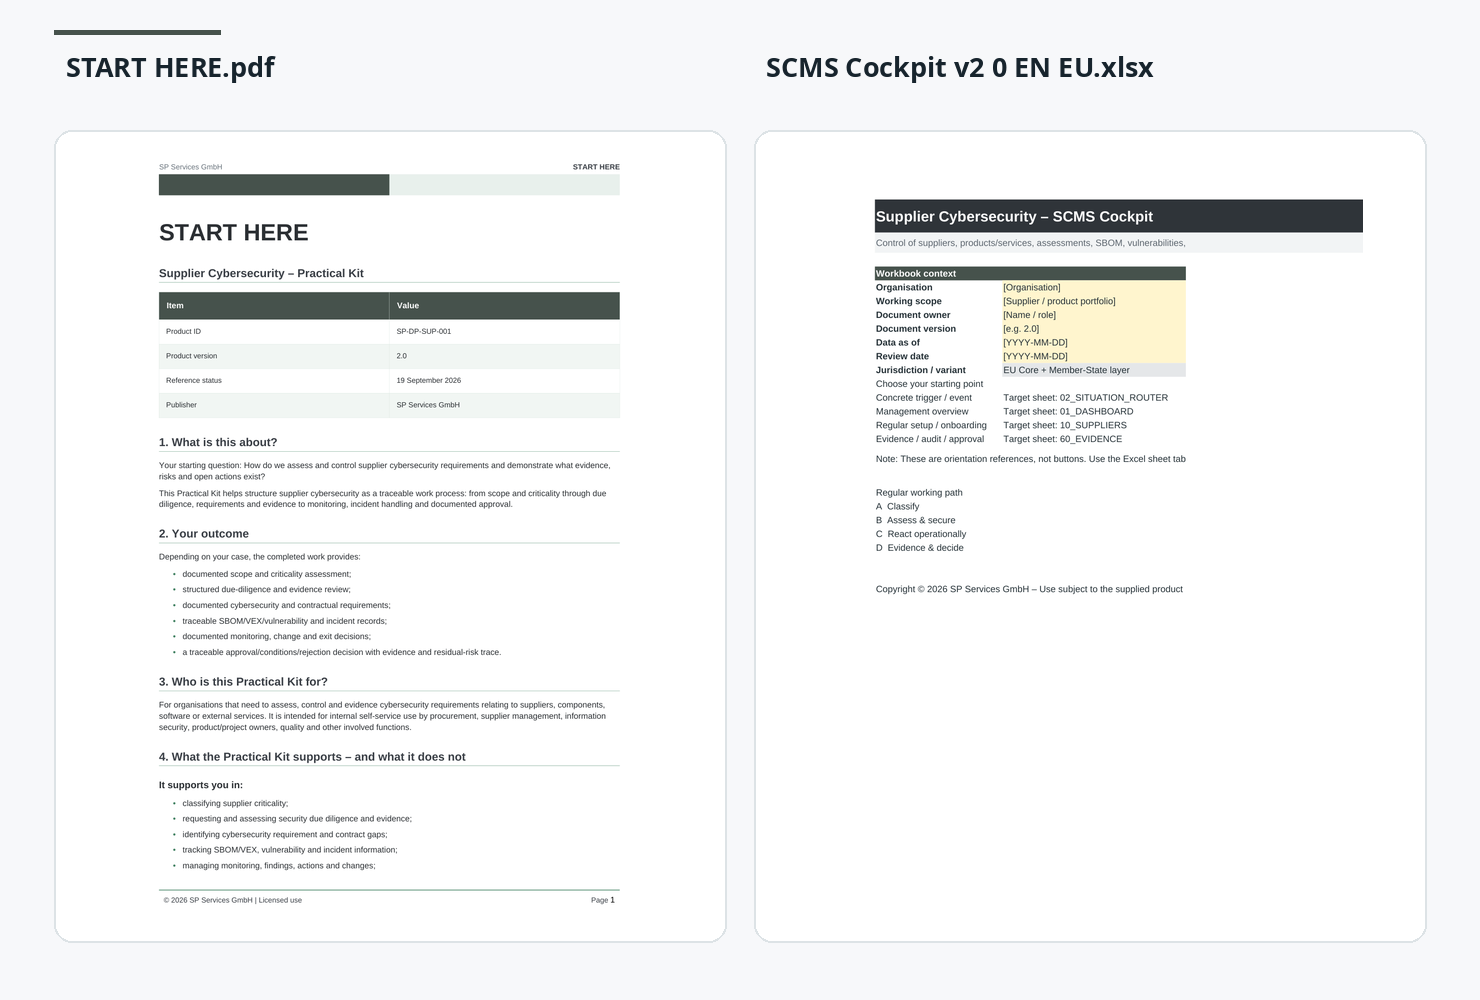
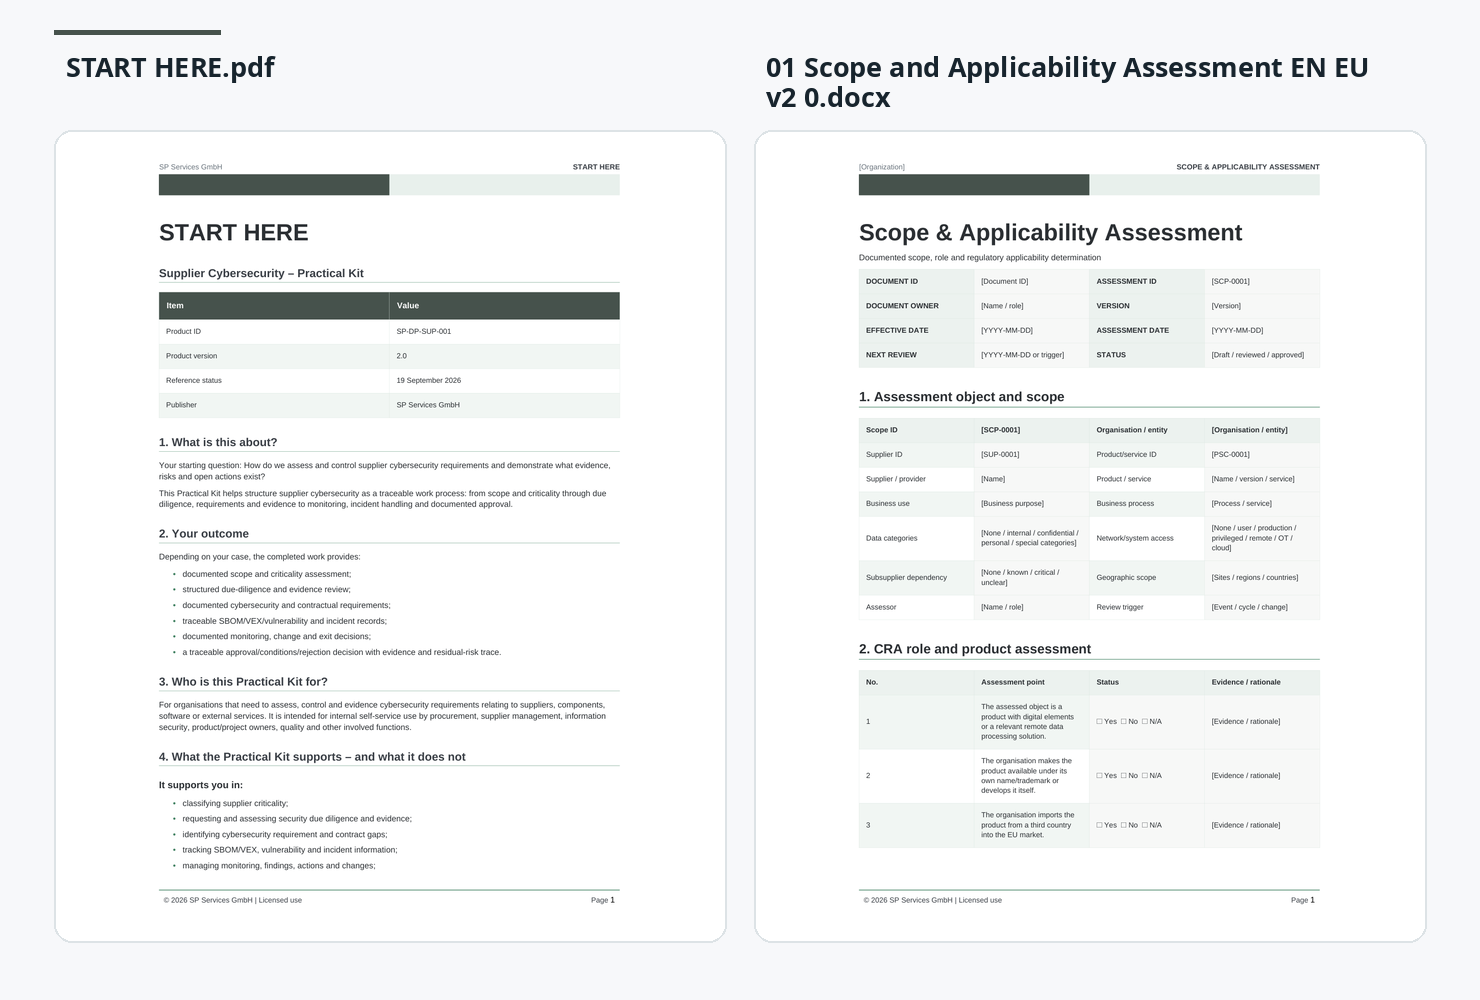
Eight connected steps bring supplier cybersecurity work into a controlled state.
Begin with a working copy and apply the process to one concrete supplier, service or technical dependency.
Read START HERE and create a controlled working copy.
Save the SCMS Cockpit as the central working file.
Capture the supplier or service case with a clear reference.
Work through scope, criticality and due diligence.
Record requirements, evidence, vulnerabilities, incidents and monitoring.
Document the decision, conditions and next review.
Perpetual internal use and editing within the named legal entity. Blank templates and source files may not be passed on.
Support for download, file access, package structure and reproducible technical product errors. No individual legal or specialist advice.
The purchased version applies. Later versions and additional content are included only where expressly stated.
Your AI can help draft and structure work, but it would still need a consistent working framework for your real case. This Kit already supplies these prepared materials: A connected supplier-security workflow with an Excel cockpit, editable supplier records, contracts/evidence tools and a worked example. That allows you and your AI to focus sooner on practical application, adaptation and review, without claiming that the Kit replaces professional judgement or guarantees an outcome.
No. It structures work and evidence but does not replace case-specific specialist assessment.
Yes. The work tools are provided for internal editing and controlled use.
No. They support structuring and review. Decisions remain human responsibilities.
Support covers download, file access, package structure and reproducible technical product errors.
€249.00 incl. VAT. Binding purchase and delivery information is available in the CopeCart checkout.